
Network interfaces and firewall
Network interfaces
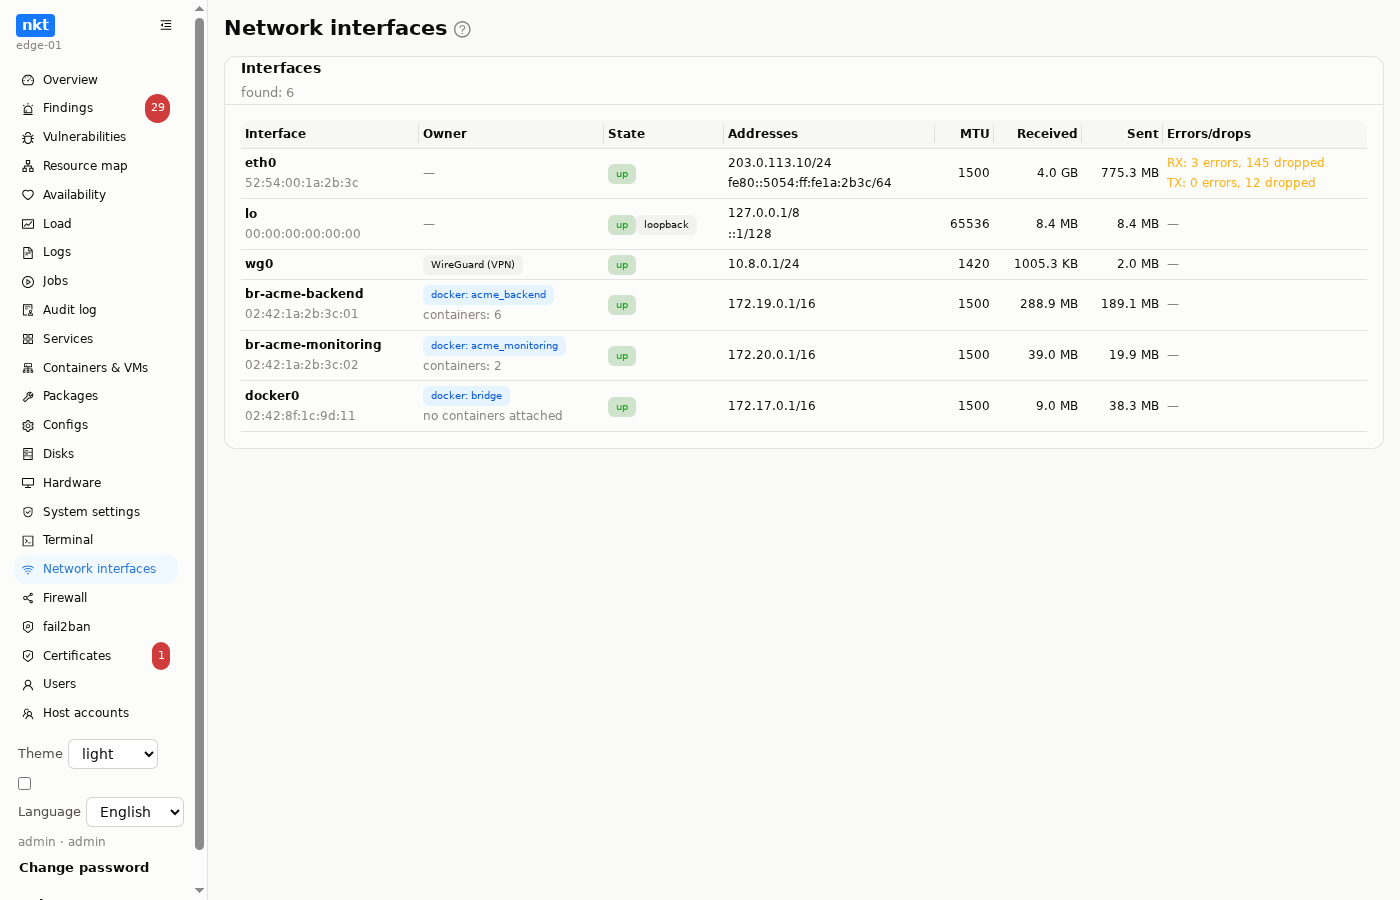
- Interfaces with addresses, state, counters and errors; the interface kind (bridge, veth, WireGuard, tunnel, libvirt) and the containers attached to it.
- Listening sockets with processes; ports open on
0.0.0.0get a one-click port check (TCP, HTTP, TLS,curl).
Firewall
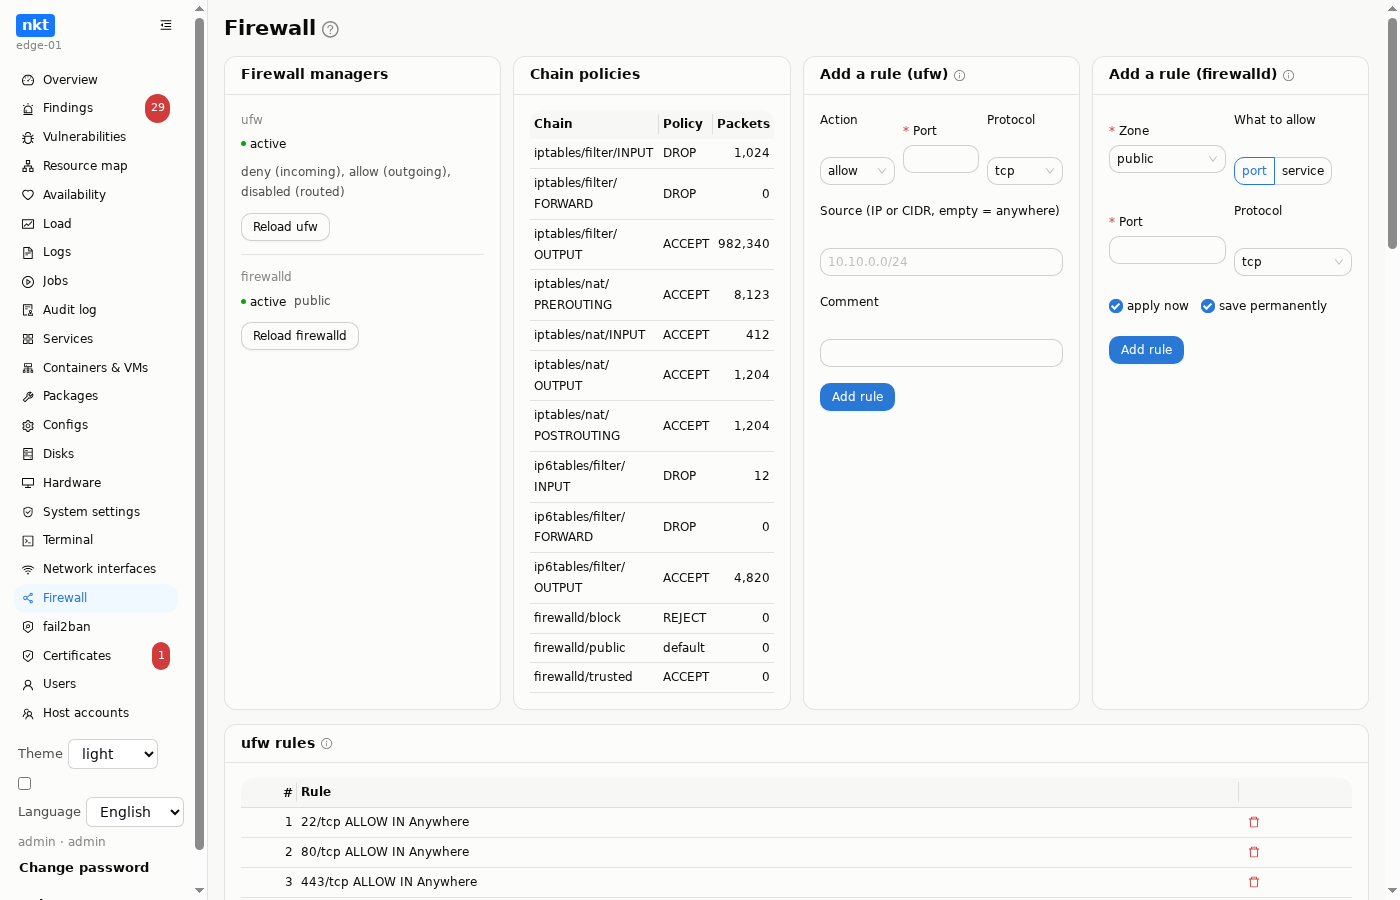
- ufw: state, numbered rules, adding and removing (port/protocol/source/comment), enabling with port 22 protection — you cannot enable the firewall without allowing SSH.
- firewalld: zones, services, ports; add and remove temporarily or permanently,
reload. - Nothing installed — ufw or firewalld is installed as a package with a live log.
- iptables is shown as is — no editing, on purpose.
Brute-force protection is a separate fail2ban section right below “Firewall”.